
Industrial Cybersecurity
What Changes When Previously Isolated Equipment Becomes Connected?
Connectivity adds operational value and a new trust boundary that requires identity, segmentation, access control, monitoring, and recovery.
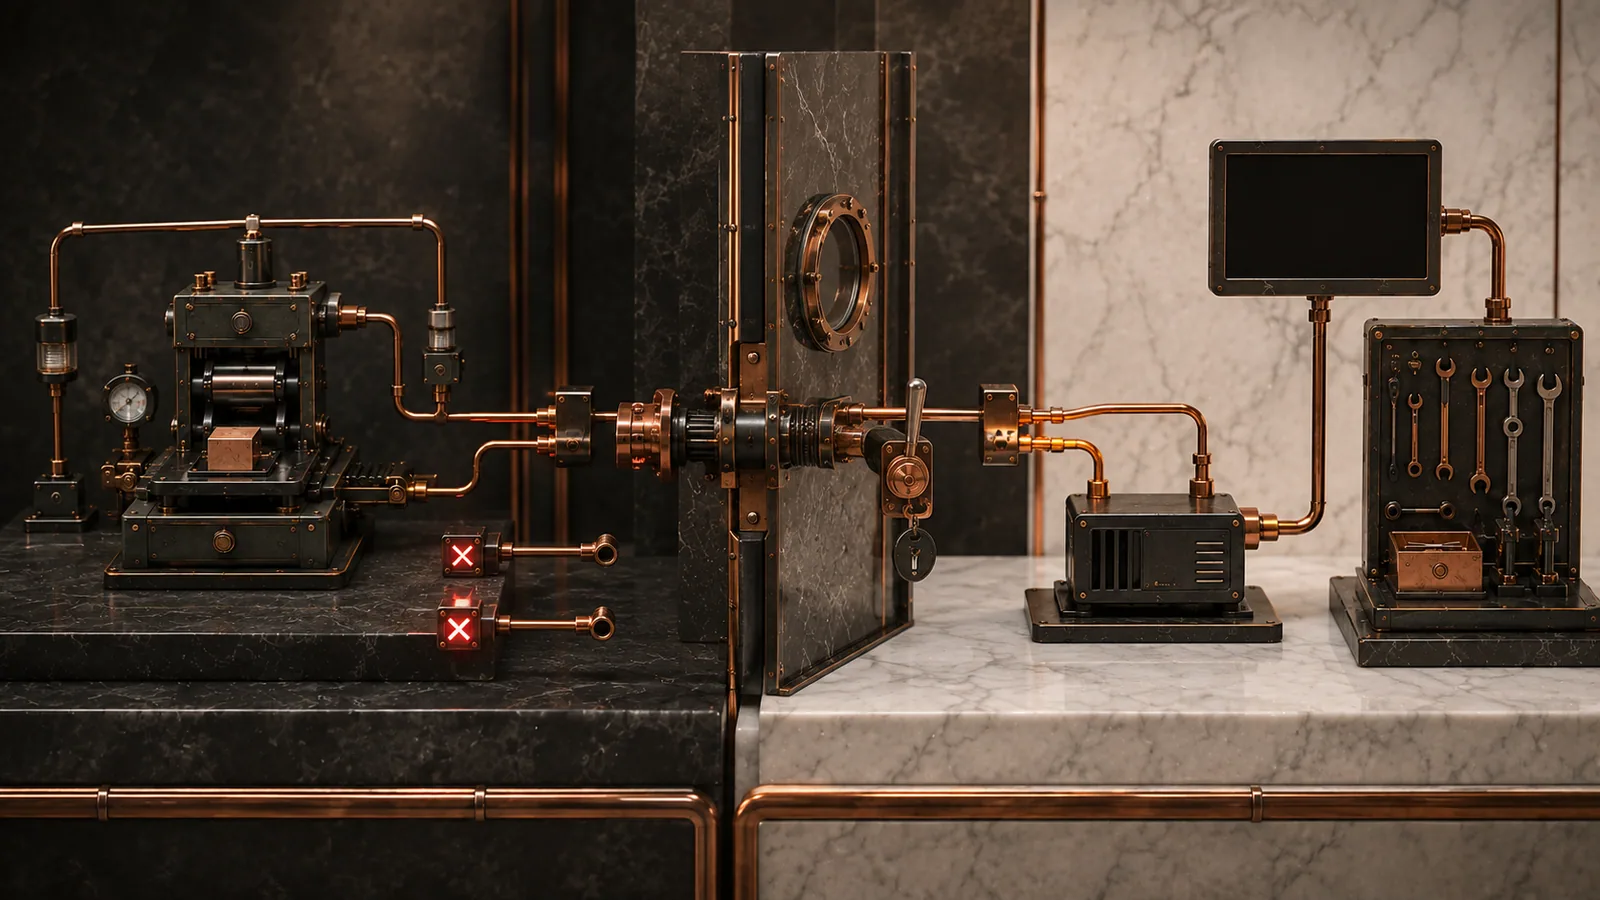
Connecting equipment changes who and what can reach it, which credentials exist, how software is maintained, where data travels, and how an external failure can affect the operation. The added pathway must be treated as part of the system design.
Industrial cybersecurity should follow the actual architecture and consequence. It is not a generic collection of controls copied from office IT, and it should not be represented as a service beyond the agreed competence and scope.
Engineering consideration
Map the new trust boundary
Document assets, users, services, networks, protocols, vendors, remote paths, data flows, and permitted direction. Separate production, management, business, and remote-access responsibilities where practical.
Engineering consideration
Control identity and access
Use individual or service identities, least privilege, protected credentials, multifactor authentication where supported, time-bounded vendor access, approval, logging, and prompt revocation.
- No shared general-user credentials
- Explicit inbound and outbound paths
- Controlled administrative access
- Credential and certificate lifecycle
Engineering consideration
Plan operational maintenance and recovery
Define monitoring, configuration backup, supported update windows, compatibility testing, rollback, incident isolation, and how the equipment continues when the connected layer is unavailable.
Questions worth answering
Before selecting the technology
- What new path reaches the equipment or its data?
- Who can administer each layer and for how long?
- How are updates tested against production constraints?
- How can the connection be isolated or recovered?
The engineering decision
Connectivity should be introduced with an explicit trust boundary, limited authority, visible operation, and a recovery plan appropriate to the physical consequence.
The correct decision depends on the operating requirement, failure consequence, available evidence, and ability to act on the result. Technology should be selected after those constraints are understood.